 asynkr
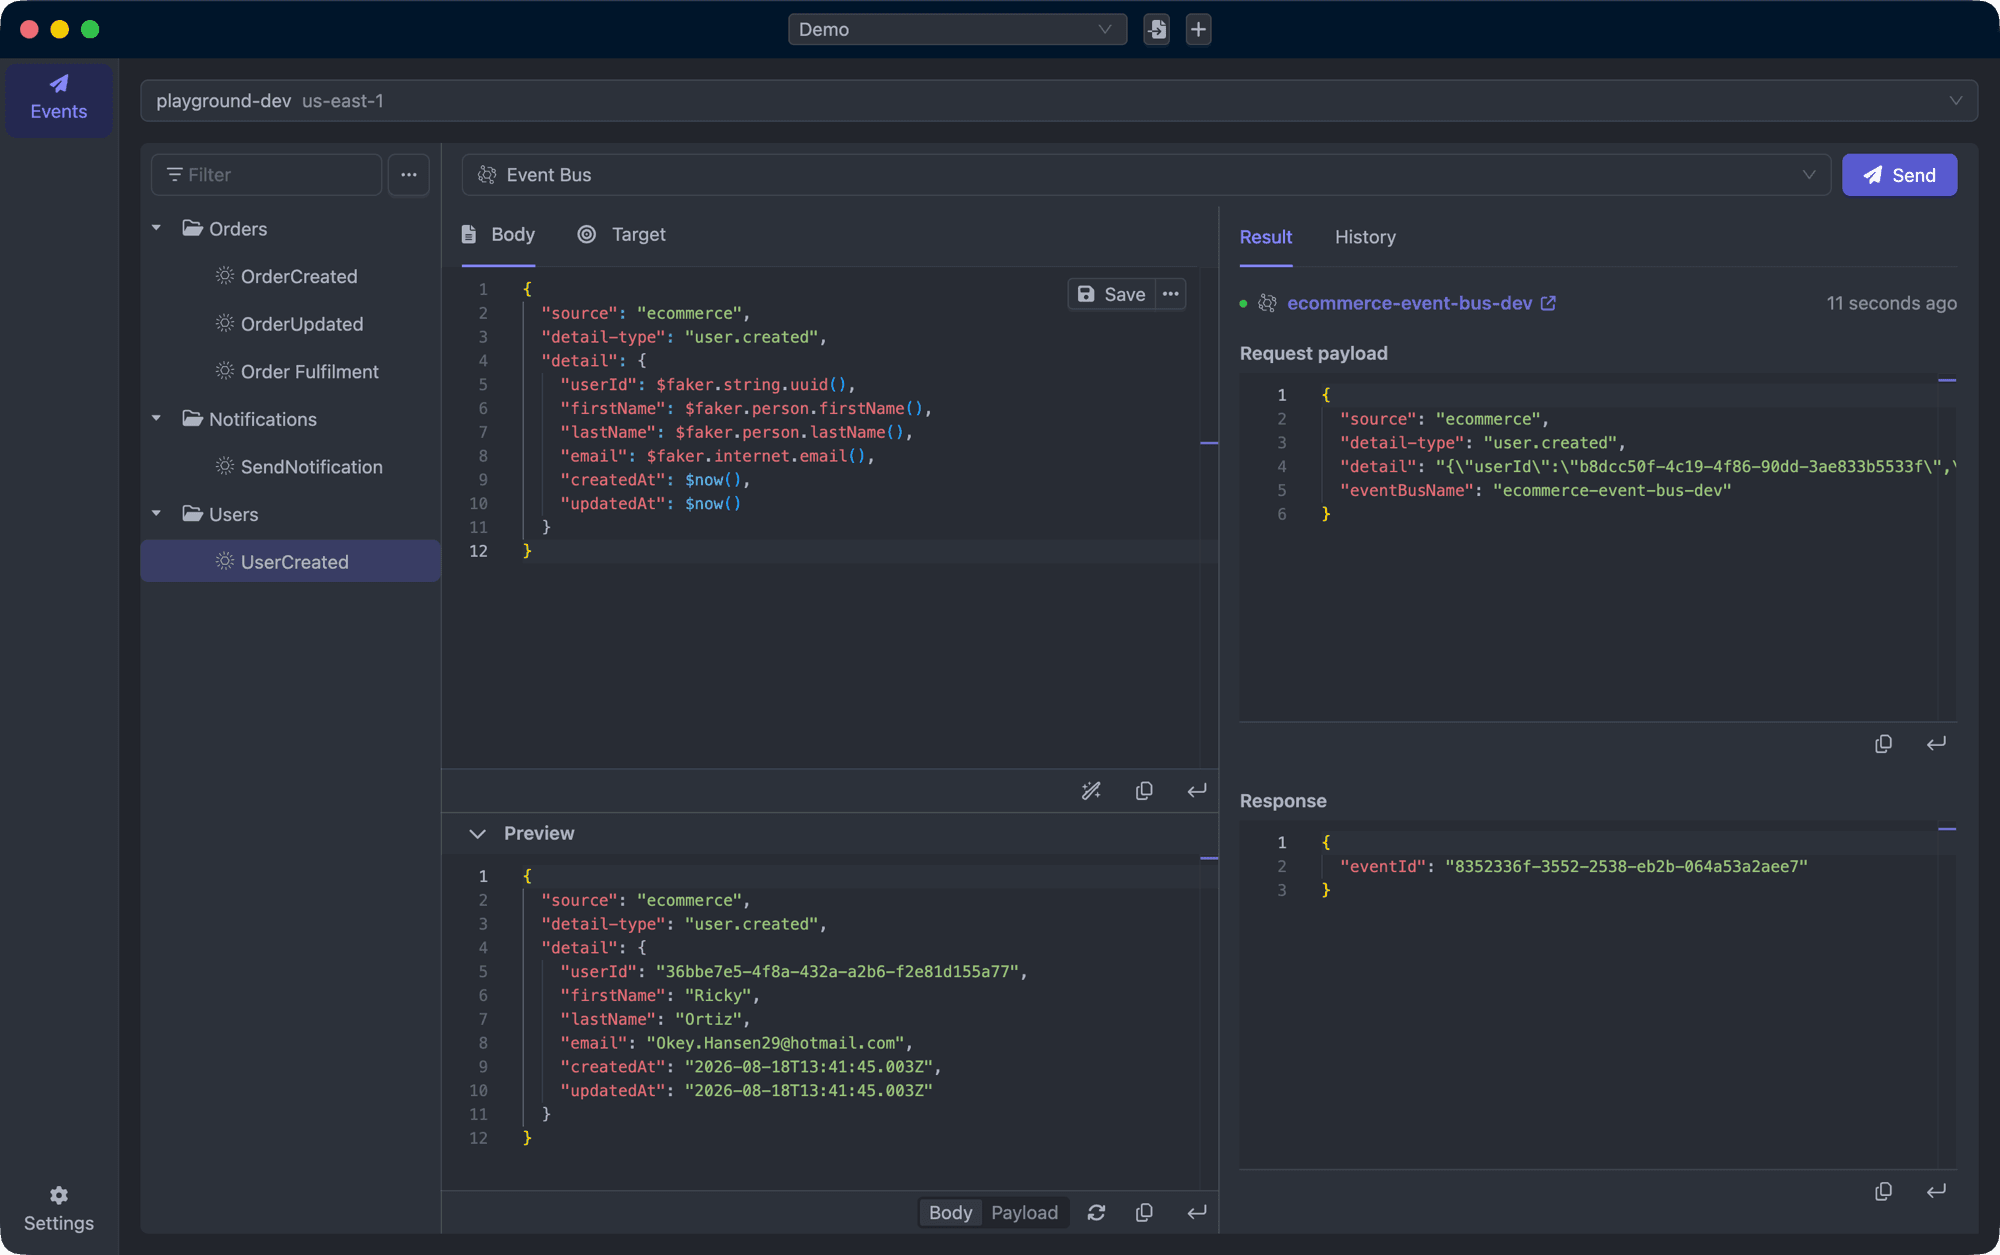
Right now, testing an event chain means five browser tabs and a shell history full of AWS CLI commands.
Built for the AWS event-driven stack
All your events in one place
Save the payloads you test constantly and reuse them any time — instead of rebuilding them from scratch or digging through the AWS console for what you sent last week.
JSONata templating
Build dynamic payloads with real expressions, not copy-pasting.
Faker.js built in
Generate realistic fake data on the fly instead of hardcoding the same three test users.
Multi-account & SSO
Switch between AWS profiles and SSO sessions without re-authenticating every time.
Envelopes for Lambda
Same event for every target — wrap it in an SQS, SNS, MSK, or EventBridge envelope to see how your Lambda handler actually parses it.
Send history & replay
Every send is logged. Replay any payload to any target in one click.
Result & Lambda logs
See the raw AWS response next to your payload, and pull up CloudWatch logs for Lambda sends without leaving the app.
One window, not ten tabs
No more switching between browsers and consoles just to send one test event.
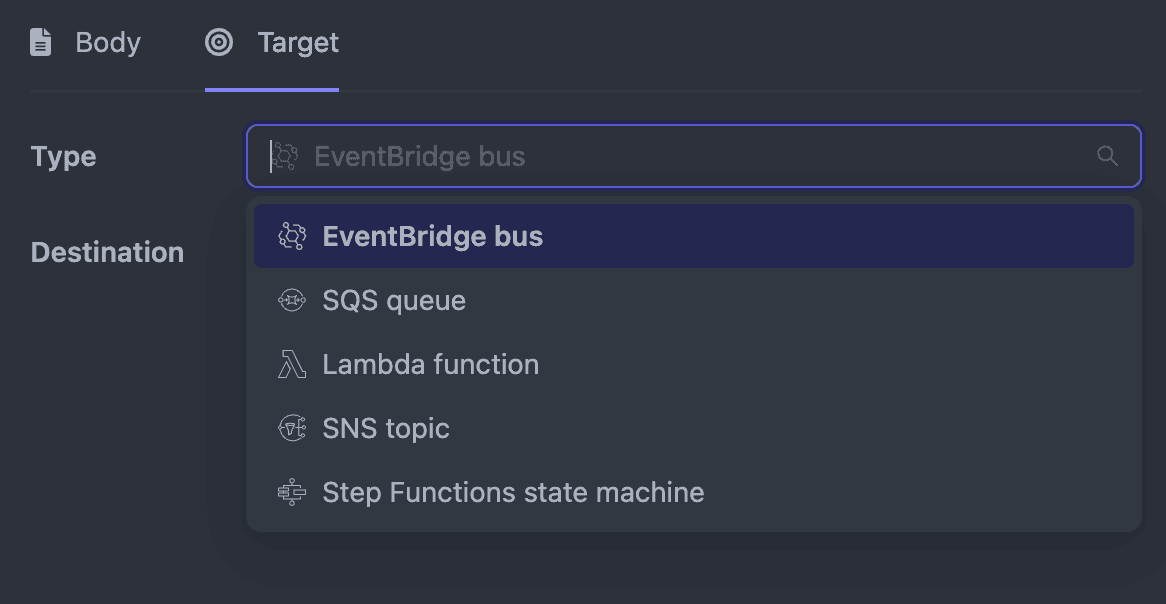
Point a payload at a real target and see exactly where it went.
Pick an EventBridge bus, Lambda function, SQS queue, SNS topic, or Step Functions state machine as the destination, preview the resolved payload, and check the result tab to confirm what actually got sent — no console tab required.
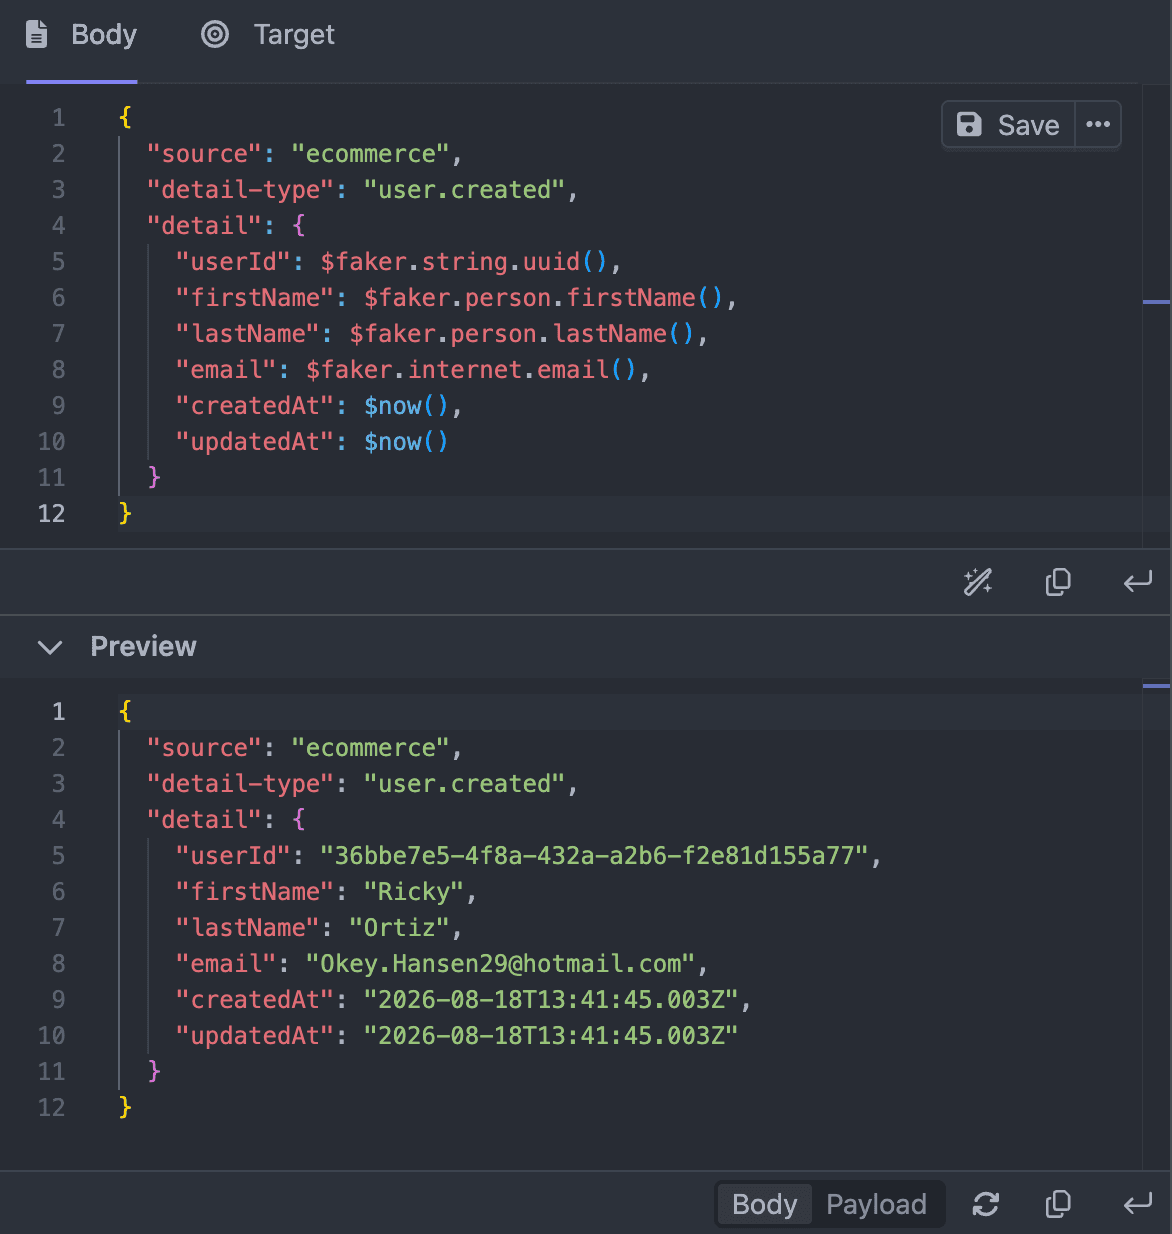
Write $faker.person.firstName(), not "John Doe" for the hundredth time.
Drop JSONata expressions straight into your payload and preview the resolved output before you send — UUIDs, timestamps, and realistic fake data generated on the fly, no copy-pasting from a spreadsheet.
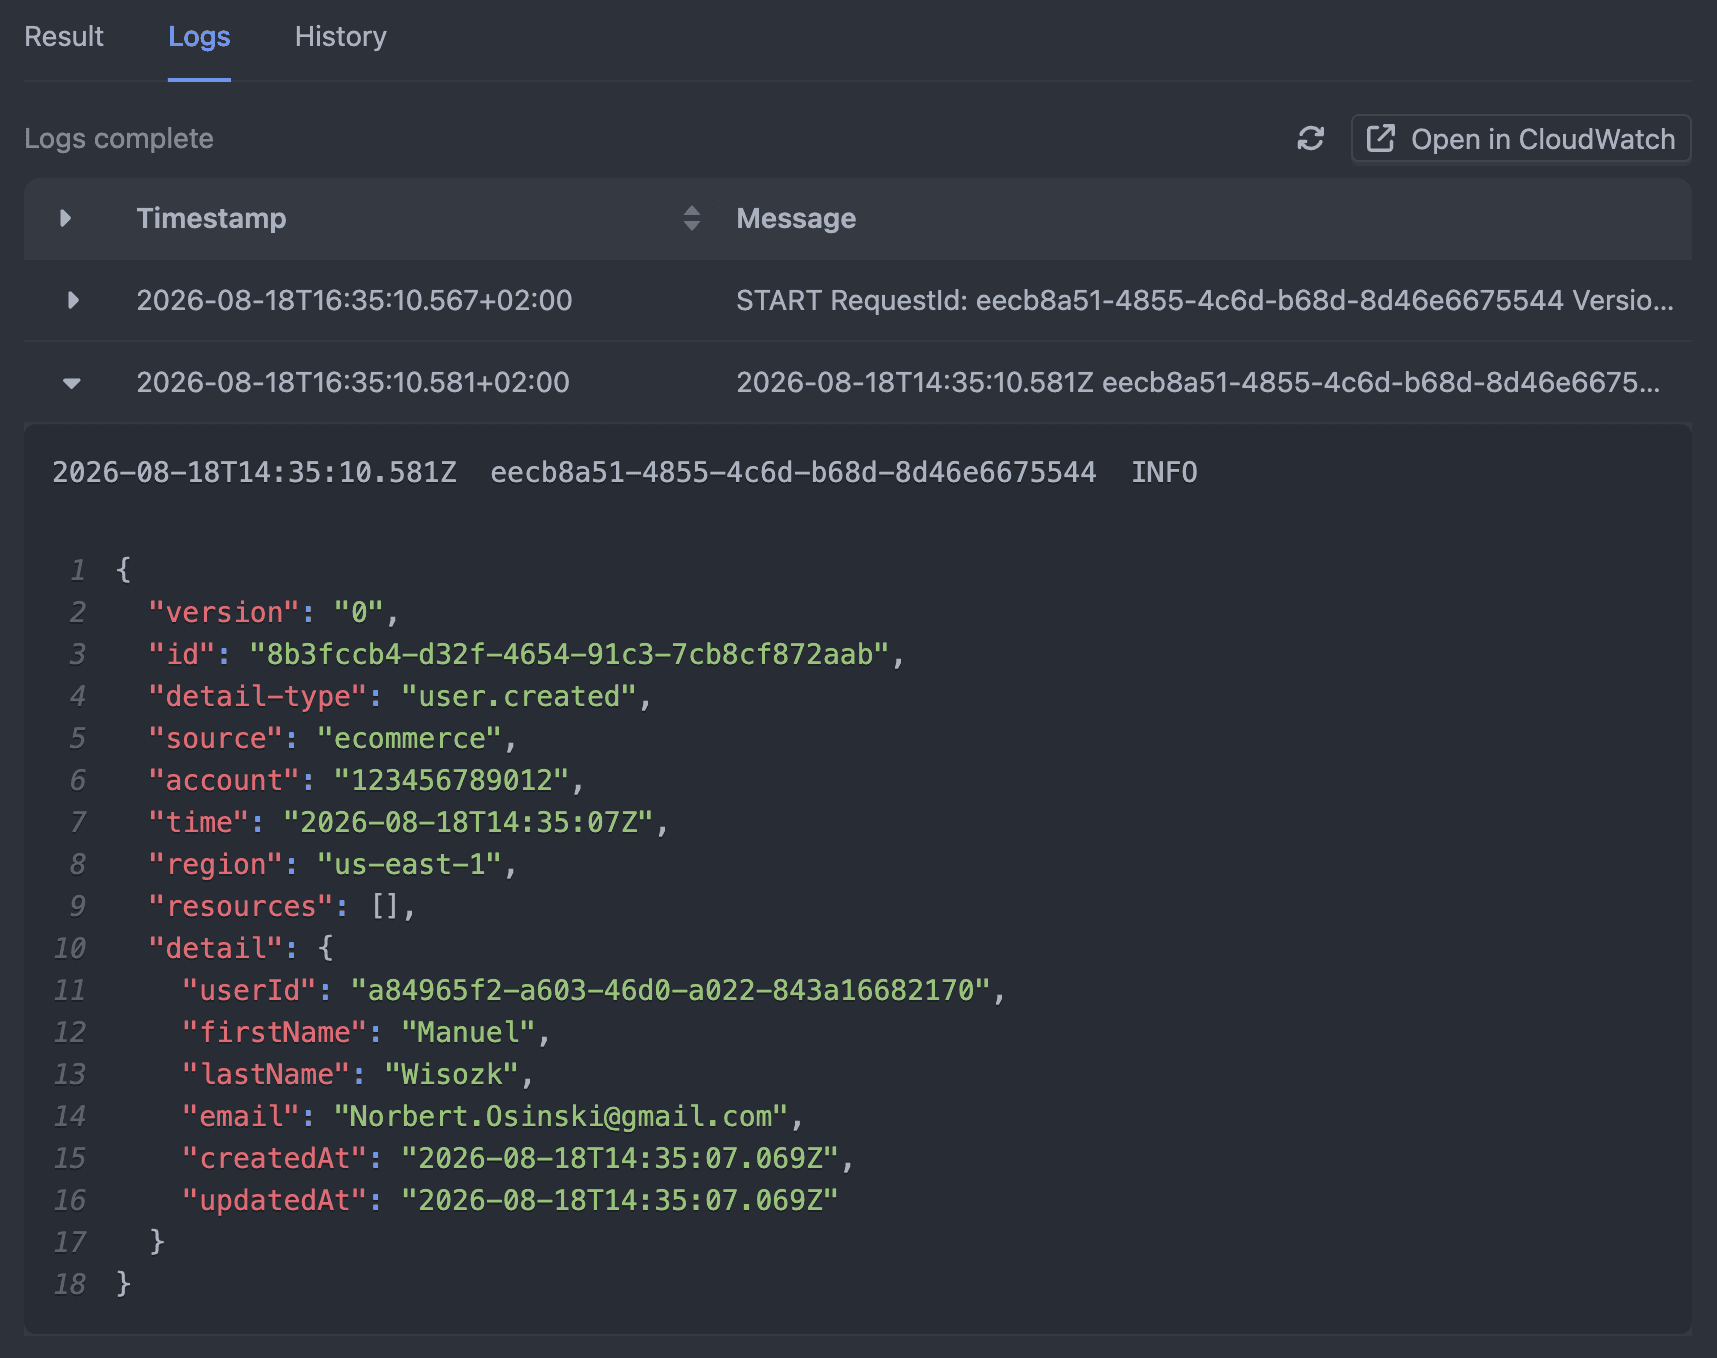
See what AWS actually did with it, down to the Lambda logs.
Every send shows the raw AWS response — or the error — right next to the payload you sent. For Lambda targets, pull up the matching CloudWatch logs without leaving the app, or jump straight to the console for that resource.
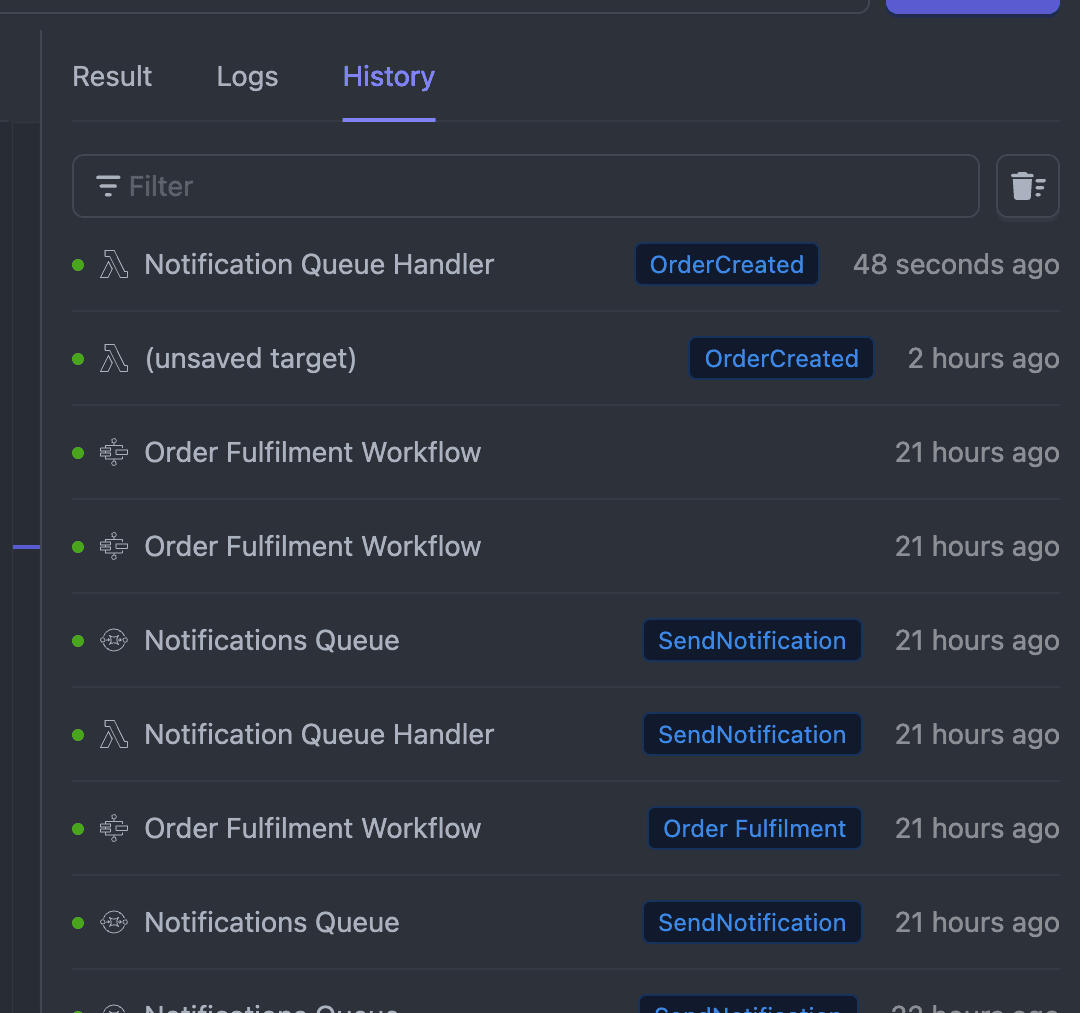
Every send, logged. Nothing disappears into a console tab.
See which target got hit, which event fired, and how long ago — across EventBridge, SQS, Lambda, SNS, and Step Functions — then replay any of it with one click instead of rebuilding the payload from scratch.
Common questions
Is Asynkr free?
Yes — free during the beta. There's no pricing tier yet; right now we're focused on feedback from engineers who deal with this daily, not monetizing early.
What AWS permissions does it need?
Only what your own AWS profile or SSO session already grants. Asynkr doesn't request any special access — it just calls the services you target (EventBridge, SQS, Lambda, SNS, Step Functions) using your existing credentials, so that profile needs read/write permissions on whatever resources you point it at (e.g. events:PutEvents on an EventBridge bus, sqs:SendMessage on a queue, lambda:InvokeFunction on a function).
Does my data ever leave my machine?
No. Asynkr is a native app — SSO authentication and every AWS call happen locally, straight from your machine to AWS. Your credentials and payloads never pass through our servers.
Which AWS services are supported?
EventBridge, SQS, Lambda, SNS, and Step Functions today, with more targets on the way.
Can I use multiple AWS accounts or SSO profiles?
Yes — switch between AWS profiles and SSO sessions without re-authenticating each time.
Free during beta.
No pricing tiers yet — just feedback from engineers who deal with this daily.
